Framework Packs
Structure NIS2, DORA, ISO 27001, EU AI Act, GDPR, SOC 2 and CRA.
REPORTACT · COMMERCIAL PARTNERSHIP
If you have to run NIS2, DORA, ISO 27001 or other regimes operationally, you do not need another checklist. You need controls, evidence, deadlines and ownership that work in day-to-day operations.
Frameworks, controls, evidence, vendor risk and reporting workflows are connected in one platform. I am your commercial point of contact for context and the next step. Subject-matter logic and delivery remain with ReportAct.
PLATFORM CAPABILITIES
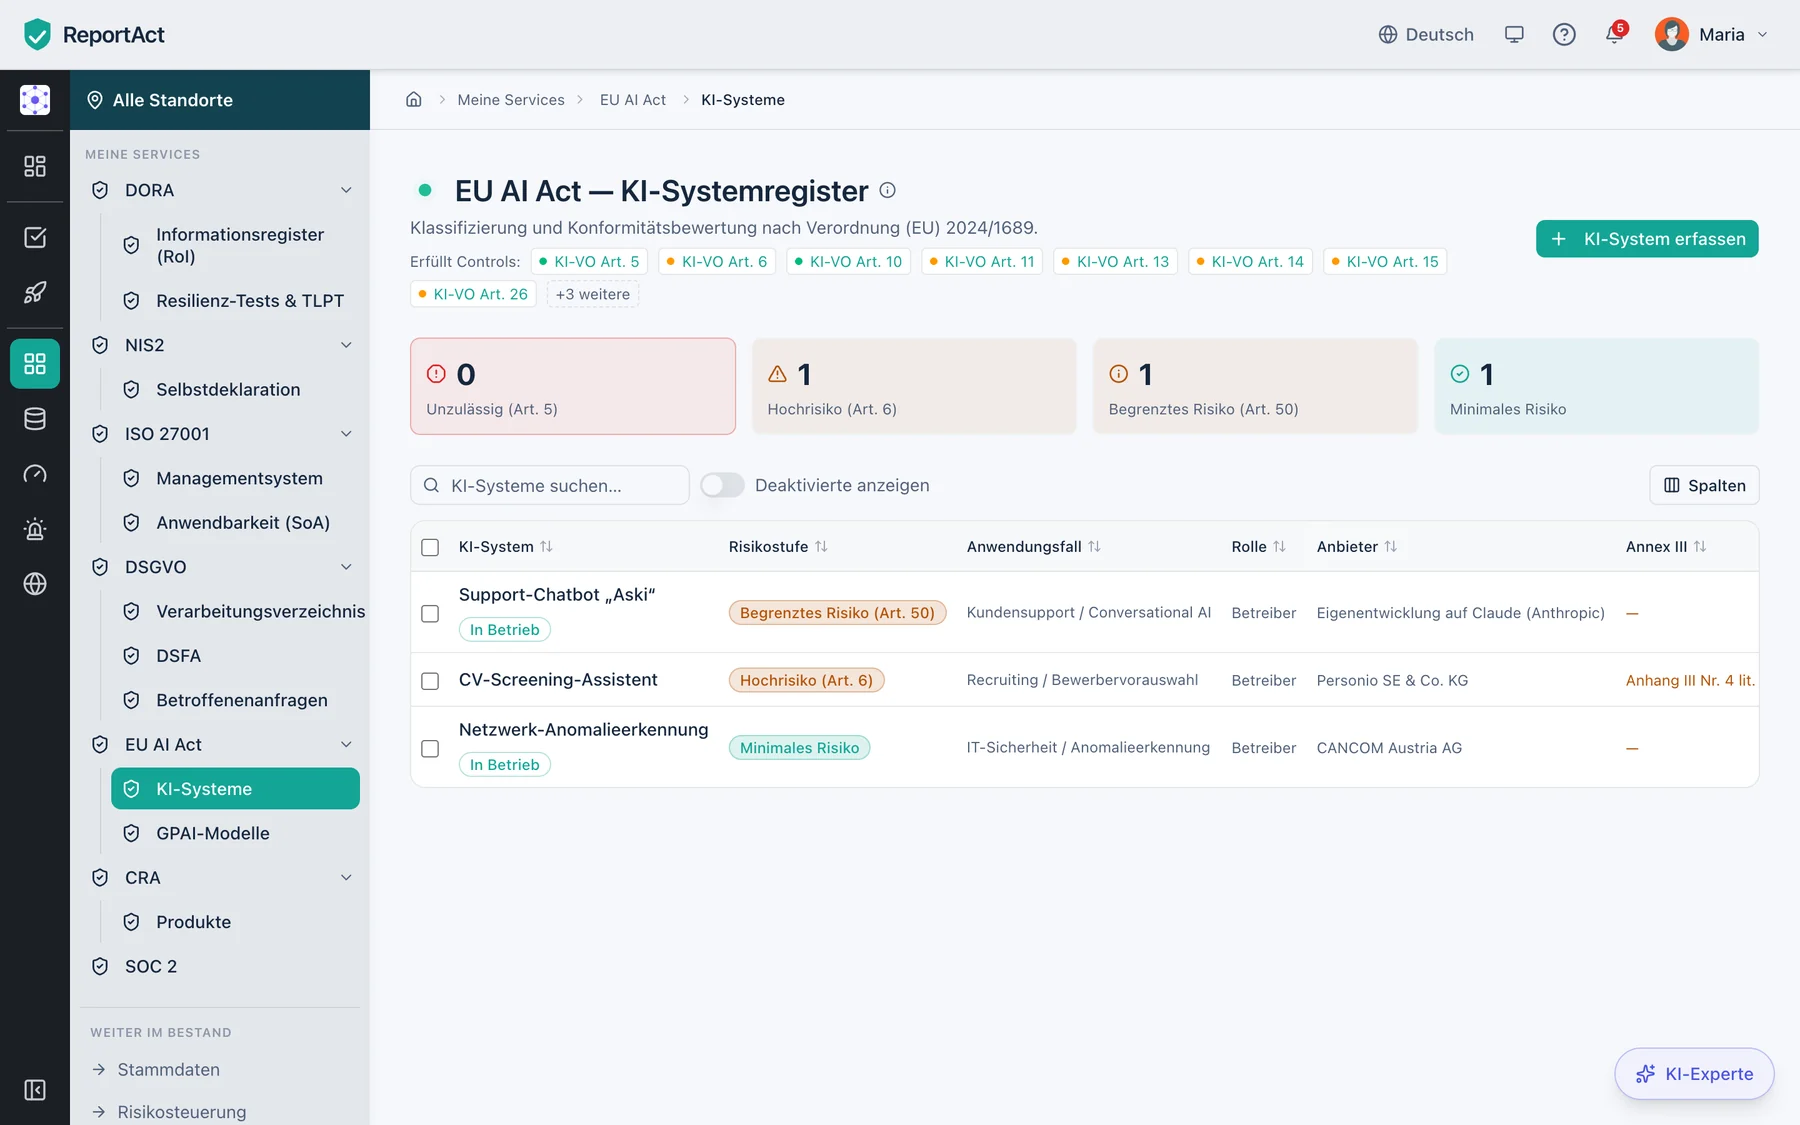
Structure NIS2, DORA, ISO 27001, EU AI Act, GDPR, SOC 2 and CRA.
Hash, chain, sign and independently timestamp evidence.
Provide curated trust information for customers and auditors.
Manage vendors, ratings, risks and registers consistently.
Organise regulatory reporting workflows and deadlines.
Handle RoPA, DPIA and DSAR through connected workflows.
Connect import, synchronisation, monitoring and automation.
Shared governance structures are possible, but legal requirements and reporting channels still need to be assessed separately for Germany, Austria and Switzerland.
Understand NIS2 across DACH →jan@reportact.comSee ReportAct on your own use case ↗